A sandbox is only as safe as its way out. Lantern ships two egress modes. The default mode enforces the allowlist inside the guest via an iptables-redirected CONNECT proxy. The optional broker mode (LANTERN_EGRESS_MODE=broker, Firecracker only) removes the network device entirely: every outbound request crosses a vsock to a broker in the runtime-manager on the host, which checks the sandbox's allowlist and adds the credential there. In broker mode the workload never holds the token it is using.
In plain termsThink of the VM as a room with no windows and one mail slot. The code inside can write a letter to any address, but the clerk on the other side of the slot only forwards letters to addresses on the list, and signs them with your name on the way out. The letter writer never learns your signature.
The workload sends an ordinary HTTP(S) request through 127.0.0.1:3128. The harness injects HTTP_PROXY/HTTPS_PROXY, so most clients need no change.
The harness (PID 1) forwards it over vsock, the VM's only channel to the host.
The broker in the runtime-manager matches the destination against the sandbox's allowlist.
If the rule has an inject entry (header + secret_uri), the broker resolves the secret on the host and sets that header, replacing any placeholder the workload sent.
The request goes upstream. A denied request is refused and written to the audit stream.
Egress in broker modeThe workload's request leaves the VM over vsock; the host broker decides, dials, and adds the credential. The VM never holds it.Opt-in: LANTERN_EGRESS_MODE=broker · Firecracker only · ADR 0026
1. CONNECT api.github.com:443
The workload uses HTTPS_PROXY=http://127.0.0.1:3128 as usual.
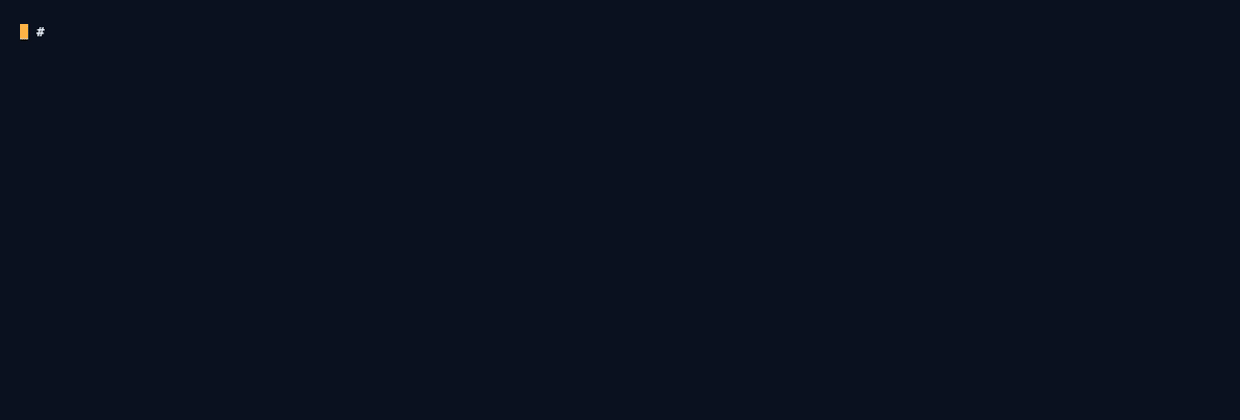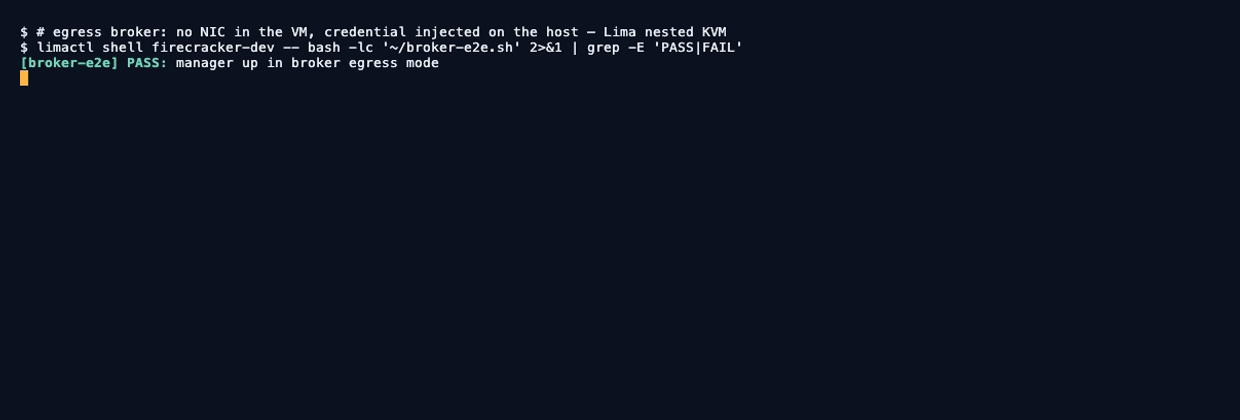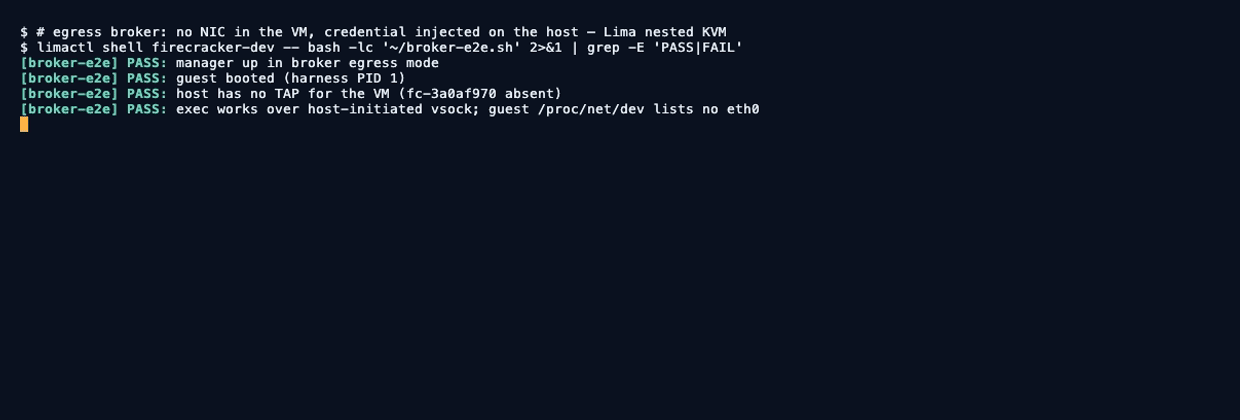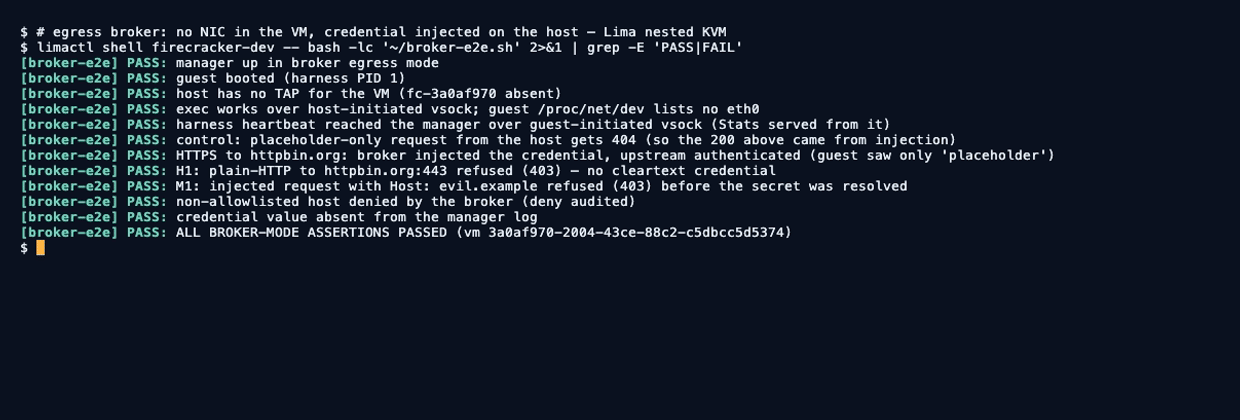
Each spawn declares its egress rules (host pattern, HTTP methods, rate). Anything not listed is denied. The broker also refuses private and metadata IP ranges and allows only port 443 unless LANTERN_EGRESS_ALLOWED_PORTS says otherwise. In broker mode (LANTERN_EGRESS_MODE=broker) the VM has no network device, so a client that ignores proxy variables simply has no route. In the default mode iptables redirects all traffic to the in-guest proxy. Denials are security-critical audit events and are never dropped, even across a brief manager outage.
Credential injection
Specs reference secrets by secret_uri, never by value. The broker resolves the ref on the host and sets the header on the outbound request, so the secret exists only on the host side of the vsock. A compromised workload cannot exfiltrate a key it never received. For HTTPS, the broker terminates TLS only for hosts whose rule injects a credential, using a per-VM ephemeral CA that is name-constrained to those hosts. Every other host is an opaque CONNECT tunnel, end-to-end TLS.
infra/firecracker/broker-e2e.sh against real httpbin.org on Firecracker 1.15.1, recorded on Lima nested KVM (aarch64). Unedited output, filtered to PASS lines.